- JavaScript 88.5%
- Rust 9.3%
- RenderScript 0.9%
- TypeScript 0.6%
- CSS 0.3%
- Other 0.2%
 3129d6448a
Some checks failed
ci.yml / fix(endo-fs-asset-server): type headers array to accept readonly baseline tuples (push) Failing after 0s
ironhorse-sanitizers.yml / fix(endo-fs-asset-server): type headers array to accept readonly baseline tuples (push) Failing after 0s
Browser Tests / browser-tests (push) Has been cancelled
CI (docs-only) / lint (push) Has been cancelled
CI (docs-only) / test (push) Has been cancelled
Copilot Setup Steps / copilot-setup-steps (push) Has been cancelled
Test project mutual dependency versions / build (push) Has been cancelled
Workflow security audit / zizmor (push) Has been cancelled
The serving-core response headers were annotated Array<[string, string]> (mutable tuples), but spread the hardened baselineSecurityHeaders, whose entries are readonly [string, string]. tsc flagged this as TS4104 in the docs/typecheck CI job (the package's local lint runs eslint only, so it did not surface locally). Widening the element type to readonly [string, string] satisfies both the spread and HttpResponse.headers, with no behavior change. Co-Authored-By: Claude Opus 4.8 (1M context) <noreply@anthropic.com> Claude-Session: https://claude.ai/code/session_01ApZmRu8mL2eZBHLEUrGoL6 |
||
|---|---|---|
| .changeset | ||
| .claude/skills/endo | ||
| .github | ||
| browser-test | ||
| c | ||
| designs | ||
| docs | ||
| evoke | ||
| go/engo | ||
| packages | ||
| pivoker | ||
| rust | ||
| scripts | ||
| .env.example | ||
| .git-blame-ignore-revs | ||
| .gitattributes | ||
| .gitignore | ||
| .gitmodules | ||
| .node-version | ||
| .prettierignore | ||
| .prettierrc.json | ||
| .yarnrc | ||
| .yarnrc.yml | ||
| AGENTS.md | ||
| ava-base.config.mjs | ||
| ava-endo-lockdown-unsafe.config.mjs | ||
| ava-endo-lockdown.config.mjs | ||
| ava-endo-shims-only.config.mjs | ||
| ava-noop-harden.config.mjs | ||
| ava-ses-shims-only.config.mjs | ||
| Cargo.lock | ||
| Cargo.toml | ||
| CLAUDE.md | ||
| CONTRIBUTING.md | ||
| eslint.config.js | ||
| LICENSE | ||
| package.json | ||
| README.md | ||
| rust-toolchain.toml | ||
| SECURITY.md | ||
| tsconfig-build-options.json | ||
| tsconfig.build.json | ||
| tsconfig.composite.json | ||
| tsconfig.eslint-base.json | ||
| tsconfig.eslint-full.json | ||
| tsconfig.eslint-src.json | ||
| tsconfig.json | ||
| tsconfig.typedoc.json | ||
| turbo.json | ||
| turbo.json.md | ||
| typedoc.base.json | ||
| typedoc.json | ||
| yarn.lock | ||
| title | group | category |
|---|---|---|
| readme | Documents | Guides |
Endo


Endo is a framework for powerful JavaScript plugin systems and supply chain attack resistance. Endo includes tools for confinement, communication, and concurrency. With Endo’s SES implementation of HardenedJS, we can opt-in to a more tamper-resistant mode of JavaScript. With Endo’s Eventual Send, we have a safe, transport-agnostic abstraction for pipelining messages to remote procedures, and concrete transports like Endo CapTP and, soon, OCapN.
Agoric and MetaMask rely on Hardened JavaScript and the SES shim as part of systems that sandbox third-party plugins or smart contracts and mitigate supply chain attacks for production web applications, web extensions, and build systems.


Endo protects program integrity both in-process and in distributed systems. Hardened JavaScript protects local integrity, defending an application against supply chain attacks: hacks that enter through upgrades to third-party dependencies. Endo does this by encouraging the Principle of Least Authority and providing foundations for the Object-capability Model.
The Principle of Least Authority states that a software component should only have access to data and resources that enable it to do its legitimate work. The Object-capability Model gives programmers a place to reason, by construction, about how permission flows through a program using well-understood mechanisms like Encapsulation.
For distributed systems, Endo stretches object oriented programming over networks using asynchronous message passing to remote objects with Capability Transport Protocols like OCapN and a portable abstraction for safely sending messages to remote objects called Eventual Send.
Security: Security-conscious JavaScript applications can use these components to improve the integrity and auditability of their own applications, improve the economics of vetting third-party dependencies, and mitigate runtime prototype pollution attacks.
Workers and Networks: Performance-conscious JavaScript applications can use these components to improve the ergonomics of message-passing between components in separate workers. Endo's Eventual Send and Capability Transport Protocols stretch asynchronous method invocation acrosses processes and networks.
Plugins: JavaScript platforms on the web and blockchains can rely on Endo to safely enable third-party plugins or smart contracts. Endo provides tooling for bundling and safely executing arbitrary programs in the presence of hardened platform objects.
Since most JavaScript libraries receive powerful capabilities from global
objects like fetch or modules like net, LavaMoat generates reviewable
policies that determine what capabilities will be distributed to third party
dependencies according to evident need, and enforces those policies at runtime
with Endo.
For distributed systems, Endo stretches object oriented programming over networks using asynchronous message passing to remote objects with the Handled Promise API and a Capability Transfer Protocol.
Between remote objects and Hardened JavaScript compartments, Endo makes distributed programs easy to program, and easy to reason about integrity. CapTP frees the programmer from needing to create bespoke communication protocols over message ports or byte streams.
Endo combines these components to demonstrate their use for a confined plugin system in the Endo Pet-name Dæmon and its CLI.
Please join the conversation on our Mailing List and Matrix. Reach out if you would like an ivitation to our meetings:
- We record a weekly Endo Sync video call .
- We recorded a weekly SES video call with the Hardened JavaScript engineering community.
- We now meet weekly with ECMA TC-39 ECMAScript Technical Committee TG-3 Security Working Group.
Core Concepts
HardenedJS introduces three components to the base JavaScript:
- Lockdown
- Harden
- Compartment
The Shared Intrinsics are a subset of the JavaScript intrinsics like the
Array and Object prototypes that, after locking down, are safe to share
between programs running in compartments.
After lockdown, programs can use harden to make other objects safe
to share between compartments.
With these three components, we can begin to rely on certain guarantees:
- Hardened objects can represent capabilities. That is, holding a reference to an object means you can use that object.
- JavaScript itself guarantees that capabilities cannot be forged. That is, a useful reference cannot be obtained by guessing its address.
- JavaScript also enforces certain structures like closures and
WeakMapcan guard capabilities. - The only way to obtain a capability is to have received it as an argument, return, global, or module of the surrounding compartmnet.
- Once hardened, an object and its methods cannot be altered.
This gives us the foundation of the Object-capability security paradigm, or simply "OCaps". From this point forward, any interesting policy can be created with code.
We can then use Endo to stretch references to Object-capabliities between processes and over networks. Instead of relying on the memory-safety of JavaScript, we then rely on cryptography to preserve confidentiality and unforgeability of references. A suitably large, signed, cryptographically random number, reachable over a network over an encrypted connection, may safely designate a capability.
Then, Endo puts ocaps directly into the hands of users with an example Petname system called the Pet Dæmon, so user's can send, receive, and use Object-capabilities with human-meaningful names.
Ruminations on the Name
- In Greek, "endo-" means "internal" or "within". This is fitting because Endo runs Node within a safe sandbox. This is fitting in turn because Endo is built on the legacy of Google Caja. In Spanish, "caja" means "box" and is related to the Latin word "capsum" and English "capsule", as in "encapsulate".
- Endo is an anagram of Node and Deno. That is to say, we are not Done yet.
- The
endocommand, like thesudocommand, is a "do" command. However, instead of escalating privilege, it attenuates privilege. - Endo lets applications endow packages with limited powerful objects and modules. As they say, you can't spell "endow" without "endo"!
- So, "E.N.Do" forms the acronym "Encapsulated Node Do".
So, just as "soo-doo" (super user do) and "soo-doh" (like "pseudo") are valid
pronunciations of sudo, "en-doh" and "en-doo" are both valid pronunciations of
endo.
Principle of Least Authority
The Principle of Least Authority (Wikipedia) states that a software component should only have access to data and resources that enable it to do its legitimate work.
PoLA explained in 3 minutes: Opening Statement on SOSP 50th Anniversary Panel, Mark Miller:
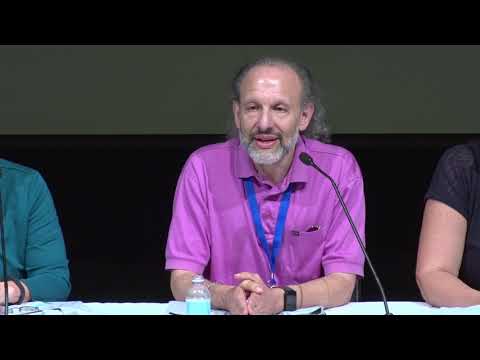
PoLA explained in 15 minutes: Navigating the Attack Surface to achieve a multiplicative reduction in risk, Mark Miller:

Bug Disclosure
Please help us practice coordinated security bug disclosure, by using the instructions in our security guide to report security-sensitive bugs privately.
For non-security bugs, please use the regular Issues page.
License
Endo and its components are Apache 2.0 licensed.